Security and data controls
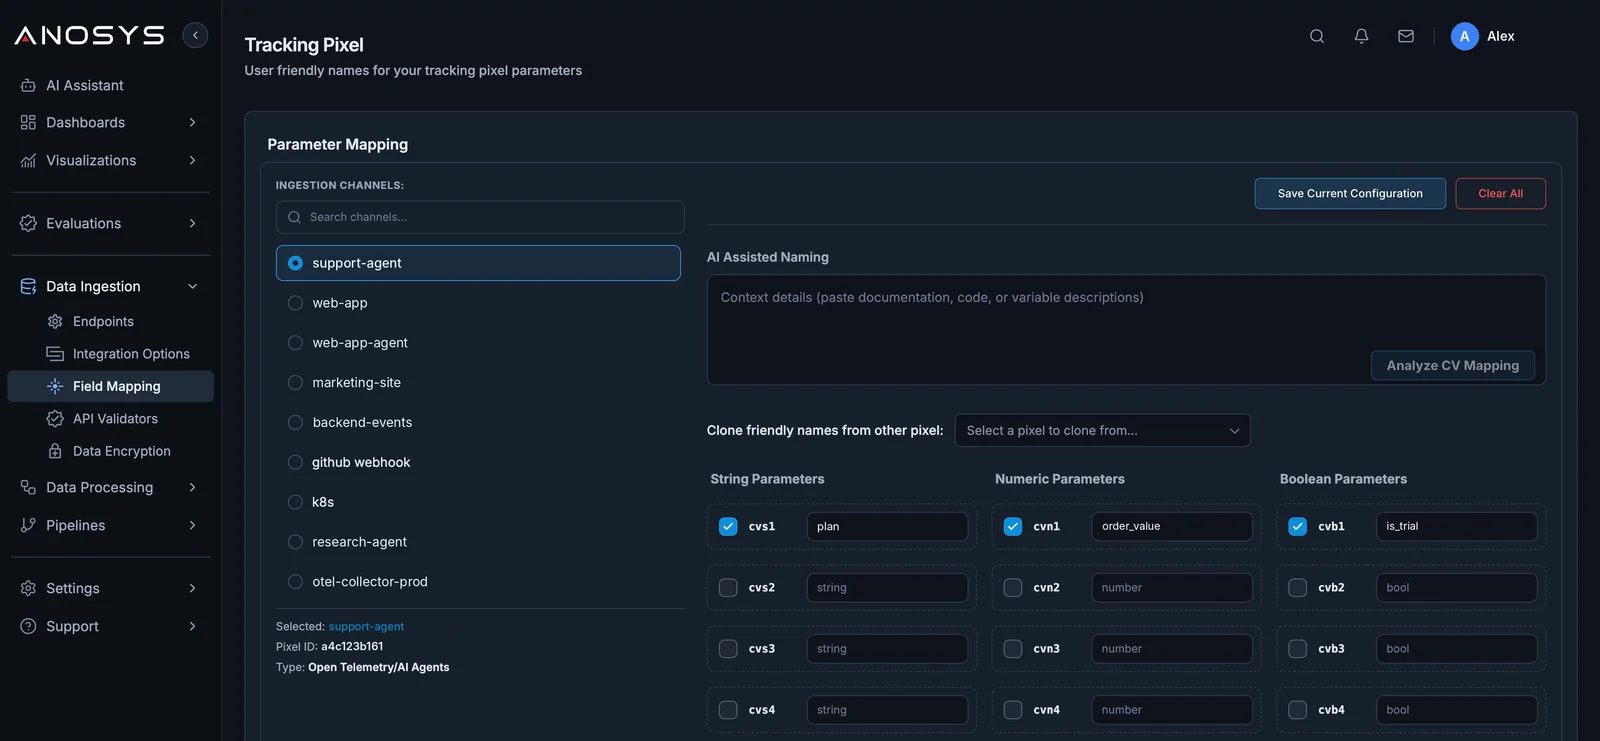
Prompts carry sensitive data
User messages and tool outputs often contain names, emails or account details. Sending all of it to another vendor is a hard sell to security.
You decide what is stored
Redaction and field mapping run before storage, encrypted fields stay unreadable without your key, and alert rules flag patterns such as emails or card numbers.
Choose what to capture, redact or encrypt the rest, set access, and alert when a rule matches.
Define
Set policy, privacy, sensitive-data, ownership, retention, and SLA requirements by workflow.
Observe
Connect those requirements to production traces, evals, tool calls, process events, and releases.
Evidence
Record exceptions, owner decisions, audit context, customer impact, and remediation steps.
Enforce
Trigger reviews, alerts, reports, or workflow controls when production behavior violates expectations.
What teams can do
- Track policy failures, sensitive data controls, audit context, and ownership
- Connect governance rules to traces, evals, workflows, and business impact
- Support enterprise deployment, security reviews, custom controls, and SLA workflows
- Protect sensitive production AI data with enterprise encryption controls
Does Anosys support enterprise security needs?
Anosys supports enterprise security and governance workflows, including sensitive data controls, audit context, and custom deployment discussions.
Can governance rules trigger alerts?
Yes. Governance and policy signals can participate in alerts, pipelines, dashboards, and incident workflows.